Cloud Security
File server moved to SharePoint? An application somebody lifted into Azure?
Each move brought settings nobody chose. Gartner puts 99% of cloud security failures on the customer's side of the line — almost all of them a default someone accepted years ago.
We fix the settings that matter without breaking what runs, then build the guardrails that stop them coming back — in Azure, AWS, GCP or the SaaS platforms around them.
You get: Roadmap, in priority order
Cloud baseline review — extract
Sample| Area | Finding | Priority |
|---|---|---|
| Identity and accessHigh |
| P1 |
| Vulnerability managementMedium |
| P2 |
| Data protection — residency, encryptionHigh |
| P1 |
| Network securityMedium |
| P2 |
| Workload protectionHigh |
| P2 |
| Logging and monitoringMedium |
| P2 |
| Incident response and continuityHigh |
| P1 |
| Governance and compliance — Loi 25Medium |
| P3 |
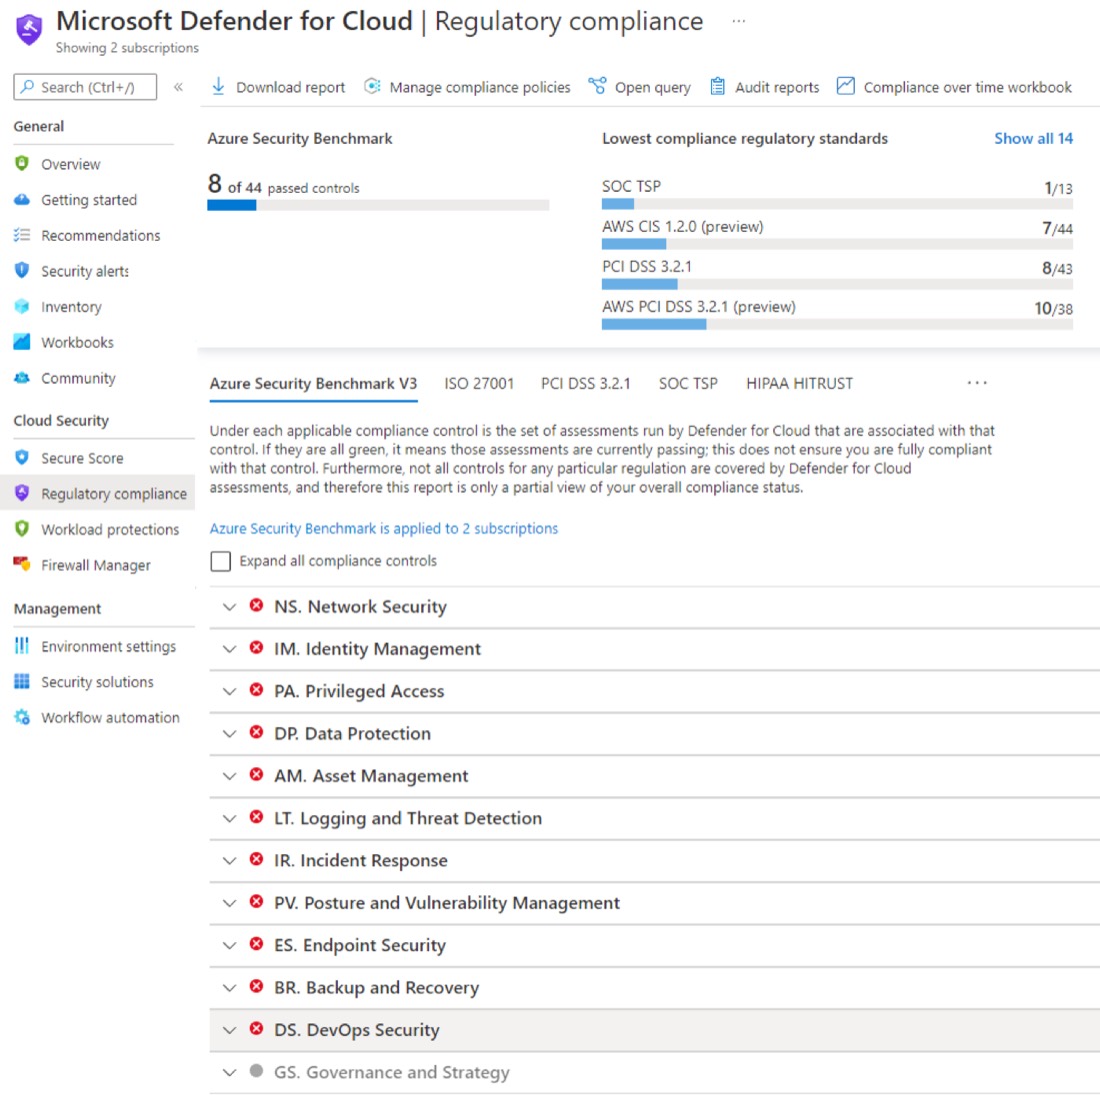
01
Assess
- Identity and access
- Vulnerability management
- Data protection — residency, encryption, key custody
- Network security
- Workload protection
- Logging and monitoring
- Incident response — including whether a restore was tested
- Governance — Loi 25 and the standards you answer to
How it runs
- Discovery workshop
- Technical evaluation against established benchmarks
- Roadmap, in priority order
02
Protect
- Identity and access — least privilege, just-in-time, conditional access
- Vulnerability management — a patch baseline, and images that get rebuilt
- Data protection — encryption, key custody, residency
- Network security — segmentation built into the topology
- Workload protection — hardened baselines as code
- Logging and monitoring — alerts that reach a person
- Incident response — backups outside the blast radius, restore tested
- Governance — policy-as-code for regions and tagging
How it runs
- Design, agreed with your team
- Build, reviewed like any change
- Handover, with runbooks
03
Maintain
- Identity and access — new privileged roles, and access that outlived its reason
- Vulnerability management — patch coverage, and what became exposed
- Data protection — new public endpoints and what sits behind them
- Network security — workloads outside the agreed structure
- Workload protection — images drifting off the baseline
- Logging and monitoring — whether diagnostics still land anywhere
- Incident response — backup success, and whether a restore works
- Governance — posture against CIS or ISO 27001
How it runs
- Drift surfaced as it happens, not at the audit
- New accounts checked on arrival
- Revisited when the architecture changes
Drowning in findings, or not sure what your cloud exposes?
Tell us what you run and we will scope the right engagement with you. Or start with the free evaluation — sixty minutes, and a written read on which domains deserve a real look. We reply within one business day.