About CyberCtrl
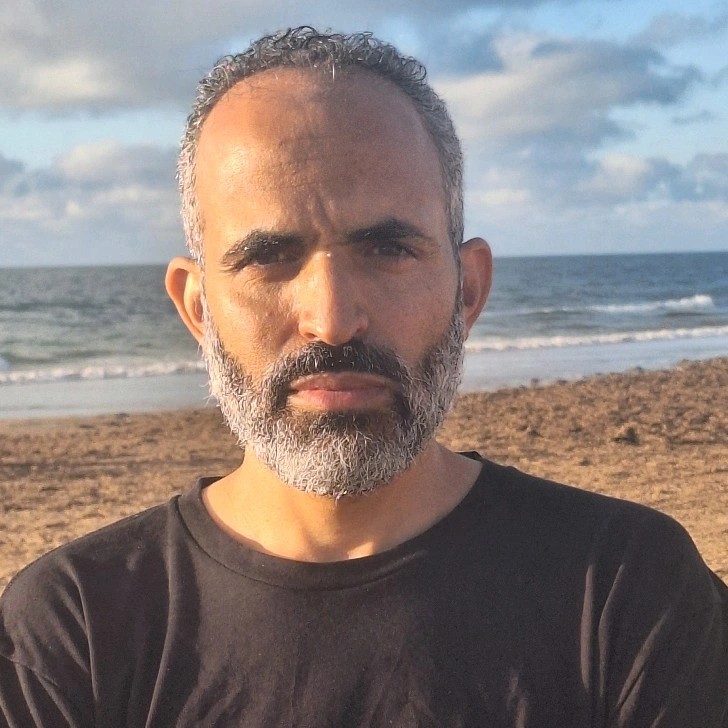
Ahmed El Ghilani
AI, Application & Cloud Security Architect
Works in French, English and Arabic
Who you will be working with
Ahmed has spent 17 years in IT security — more than 10 of them in application and cloud security, and the last three securing enterprise AI platforms. He works in the places where security either holds or quietly fails: the delivery pipeline, the cloud platform, and the AI tooling that now writes a growing share of the code.
That work has been done inside a large public utility, a municipal government, a provincial ministry and a national telecom. He led the security governance that took GitHub Copilot from a blocked pilot to an approved, monitored rollout; designed and implemented secure Azure landing zones for Ville de Québec and the Ministry of Justice; and ran the firewall migration behind a 4G network serving more than six million subscribers, without an interruption.
CyberCtrl exists because the controls that make those environments defensible are not enterprise-only. They are the same controls a hundred-person company needs and has nobody to build — and they cost far less to put in before an estate has grown around their absence.
Certifications
- Microsoft Certified: Azure Administrator Associate (AZ-104)
- AWS Certified Solutions Architect – Associate
Education
- MBAConcordia University, Montréal, 2021
- M.Sc.A, Network EngineeringÉcole de technologie supérieure (ÉTS), Montréal, 2012
- B.Sc, Telecommunications EngineeringInstitut National des Postes et Télécommunications, Rabat, 2006
Our approach
We combine offensive testing with secure architecture and enablement — reducing risk while keeping delivery moving. Findings come with the fix, and we stay through remediation rather than handing over a report.
Held across our consultants
The bench we draw on, by discipline. These are held by the consultants who deliver the work, not by any one person.
- OSCPOffensive security
- OSWEWeb exploitation
- AWS Security SpecialtyCloud security
- Microsoft Cybersecurity Architect Expert (SC-100)Cloud security architecture
- Microsoft Azure Security Engineer Associate (AZ-500)Azure security engineering
- CISSPSecurity architecture & management
- CISMSecurity management
- CISAInformation systems audit
- PCI-QSAPayment compliance
- ISO 27001 Lead ImplementerGovernance
How we work
Practitioners, not presenters
The person who scopes your engagement is one of the people who delivers it. You talk to a consultant who does this work, not a sales lead who hands you over once the contract is signed.
Crown jewels first
Nobody can protect everything equally, and pretending otherwise is how security budgets get spent in the wrong order. We work out what the business genuinely cannot lose, and start there.
Sized to your organisation
We have built these controls at utility and municipal scale. The useful part of that is knowing which of it applies to a team of twenty — and which of it is overhead you should not pay for.
Credentials that hold up
OSCP and OSWE on the offensive side. AWS and Microsoft cloud security certifications on the build side. CISSP, CISM, CISA, PCI-QSA and ISO 27001 Lead Implementer across management, audit and governance.
We leave systems, not slides
Findings are only useful once they are fixed. We stay through remediation and build the pipeline checks that stop the same issue coming back.
What we do
- AI
Copilot and AI agents are already running. We scope what they can reach, fit the rollout to how your teams actually work, and licence for what you need rather than what the vendor bundles.
- Microsoft 365 & Workspace
Nobody ever configured it — so access is too wide, sharing is open, there is no backup, and licences are billed for people who never touch half of them. We fix the configuration and right-size the count.
- Audits & Questionnaires
An auditor found something, or a client sent a questionnaire — and the deal is waiting on an answer nobody inside can give.